MacSync malware hides payloads in public iCloud calendars
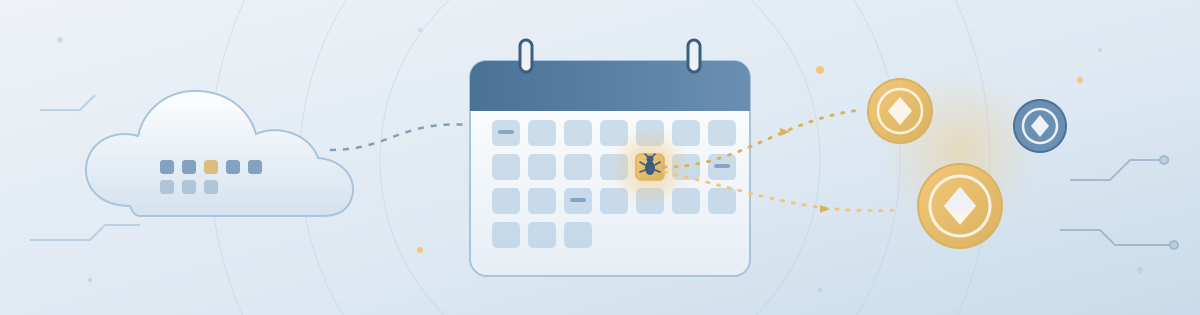
A newly spotted variant of the MacSync infostealer is using public iCloud calendar events to deliver its next-stage payloads to macOS systems, according to Kaspersky researchers.
MacSync is written in Swift and first appeared in April 2025. It has recently been pushed through ClickFix campaigns, in which victims are tricked into running commands themselves. Those lures posed as Homebrew and as macOS tools for analysing disk space. Kaspersky says earlier versions of MacSync were derived from the AMOS stealer family. Since then, the malware has grown through additional modules.
A fake crypto wallet as bait
The operators rely on social engineering. Besides ClickFix-style attacks, they offer MacSync disguised as free or cracked software, or as brand-new applications.
Sponsored Recommended for you – discover more →